Compliance Management KPIs: A Practical Guide

Michael Iyiola
Co-Founder, CWORT
Discover practical key performance indicators for compliance management to measure control effectiveness, eliminate vanity metrics, and reduce risk exposure.
A dashboard can show every training session completed and every policy acknowledged, yet leave leadership unable to answer the question that matters: are controls reducing exposure? Key performance indicators for compliance management that count activity alone create an appearance of control, not evidence of effectiveness.
That gap is familiar to compliance teams. Evidence sits across tools and departments, while metrics often track what is easiest to count rather than what demonstrates control performance. Without clear definitions, accountable owners and traceable evidence, a rising completion rate cannot show whether a weakness has been addressed or risk remains unresolved.
This guide explains how to define, compare and put meaningful compliance KPIs into practice. You will learn how to link indicators to control outcomes, evidence quality, ownership and remediation, and how to distinguish useful measures from vanity metrics. It also explores how structured evidence and reproducible scoring can support a consistent view across mapped frameworks. The aim is a reporting approach that gives leadership and assurance teams a defensible account of progress, control effectiveness and remaining exposure.
Key Takeaways
- Choose key performance indicators for compliance management that reflect defined objectives and material risks, not simply the volume of completed tasks.
- Document each KPI’s calculation, scope, data source, owner and reporting cadence so results can be interpreted consistently.
- Use leading indicators to inform preventive action and lagging indicators to assess outcomes. Neither alone provides a complete view.
- Assign responsibility for capturing, validating and interpreting KPI data, with clear escalation when results signal unresolved exposure.
- Connect measures to control outcomes and traceable evidence. A structured platform such as CWORT can support consistent, reproducible reporting.
Table of Contents
- What are key performance indicators for compliance management?
- How to design reliable compliance management KPIs
- Which compliance KPIs are most useful? Compare indicator types
- How to put compliance KPIs into practice and report them
- How CWORT supports evidence-backed compliance KPI management
What are key performance indicators for compliance management?
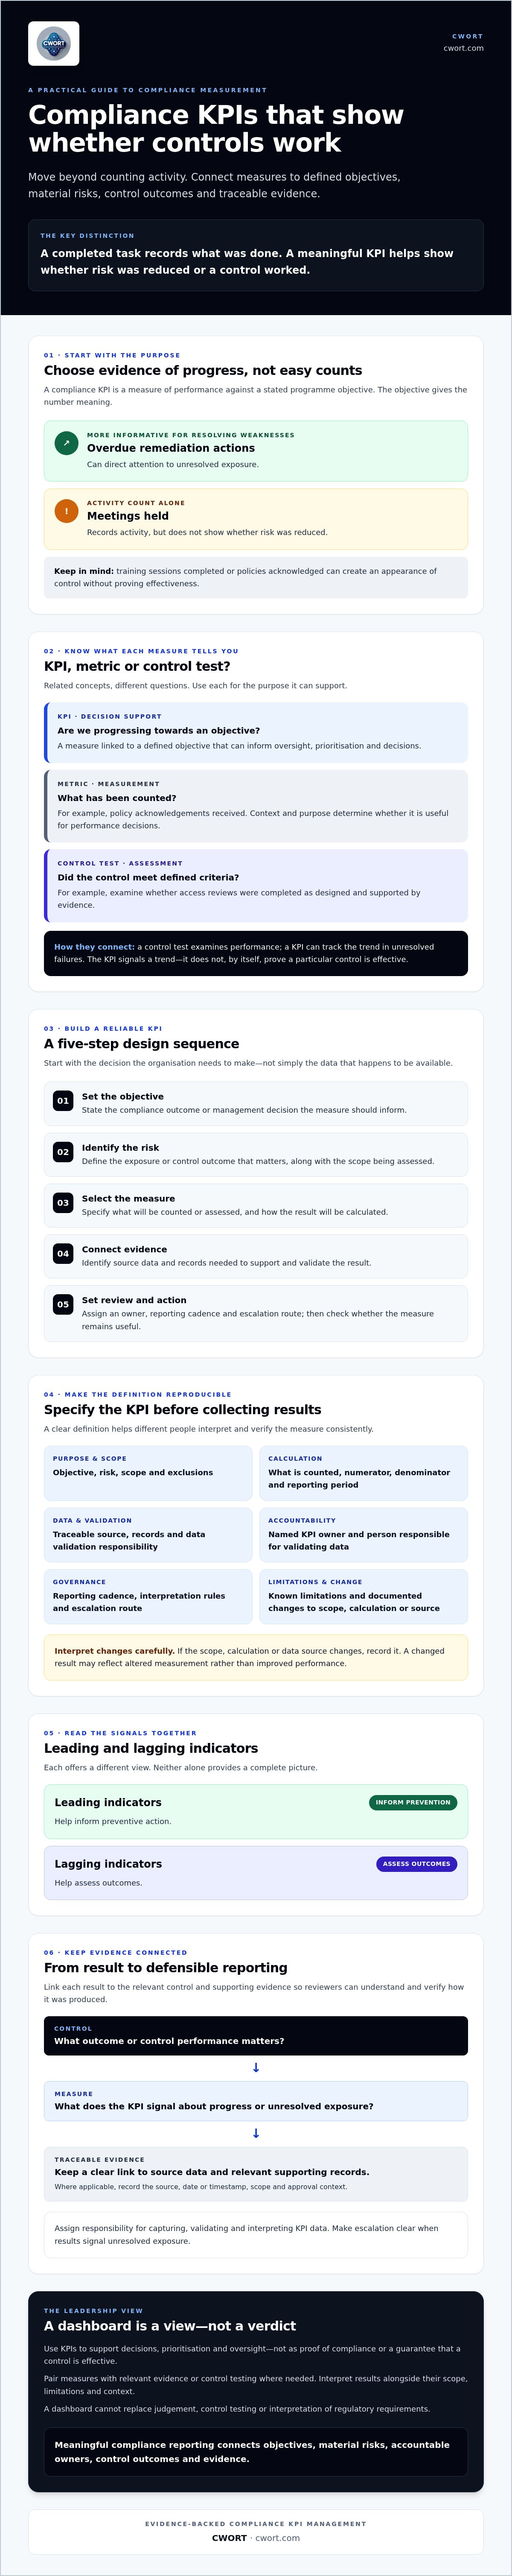
A compliance KPI is a measure used to assess how well a compliance programme is performing against a stated objective. That objective gives the number meaning. For example, if the goal is to resolve identified control weaknesses, a measure of overdue remediation actions is more informative than a count of meetings held. The first can direct attention to unresolved exposure; the second records activity without showing its effect.
A compliance KPI measures progress towards a defined programme objective. A raw activity count records what was done, not whether risk was reduced or a control worked.
This distinction matters when selecting key performance indicators for compliance management. A programme-level KPI can signal where oversight or resources are needed, but it does not, by itself, prove that a particular control is effective. That requires relevant evidence and assessment against defined criteria. KPIs support decisions and prioritisation; they do not guarantee compliance or replace professional judgement.
Compliance KPI, metric or control test: what is the difference?
These terms are related, but they answer different questions. A performance indicator or key performance indicator (KPI) is a decision-support measure linked to an objective. A metric is any measurement, such as the number of policy acknowledgements received. It becomes useful for performance decisions only when its context and purpose are clear.
A control test evaluates a control against defined criteria. For example, a test may examine whether access reviews were completed as designed and supported by evidence. A KPI could track the proportion of identified review failures that remain unresolved. The KPI signals a trend; the test examines control performance.
Why compliance teams measure performance
Well-designed measures help leaders oversee programme objectives, prioritise risk and hold owners accountable for remediation. They make change visible across reporting periods, provided the definition stays stable. If the scope, calculation or data source changes, record that change. Otherwise, a movement in the result may reflect altered measurement rather than improved performance.
Set the purpose before choosing the number. Define what is included, how it is calculated, who validates the data and what decision a result should inform. A dashboard can bring information together, but it cannot replace judgement, control testing or interpretation of regulatory requirements. Treat it as a view of evidence and signals, not a verdict on compliance.
How to design reliable compliance management KPIs
Build each measure from a decision the organisation needs to make, not from data that happens to be available. Use this repeatable sequence:
- Set the objective: State the compliance outcome or management decision the measure should inform.
- Identify the risk: Define the exposure or control outcome that matters and the scope being assessed.
- Select the measure: Specify what will be counted or assessed, and how the result will be calculated.
- Connect evidence: Identify the source data and records needed to support and validate the result.
- Set review and action: Assign an owner, reporting cadence and escalation route, then check whether the measure remains useful.
For example, a KPI about control-review completion should state which reviews are in scope and what qualifies as complete. A completion figure alone may not reveal whether the review met the expected standard. Pair it with relevant evidence or a control test where needed.
Specify each KPI before collecting data
Document the purpose, numerator, denominator, exclusions and reporting period before gathering results. Name the accountable KPI owner and the person responsible for validating the source data. These roles may be different. Record limitations, interpretation rules and changes to the calculation so a revised figure is not mistaken for a change in performance.
Every KPI needs an accountable owner and a traceable source. Someone should be able to explain the result, and reviewers should be able to verify how it was produced.
Connect indicators to evidence and control outcomes
For each result, retain a clear link to the relevant control and supporting evidence. Record the source, date or timestamp, scope and approval context where applicable. This makes it possible to distinguish a supported result from an estimate and to investigate gaps rather than relying on a dashboard figure alone.
Set a baseline using a defined period and consistent method. Then establish thresholds that reflect the organisation’s risk appetite, control context and decision needs. There is no universal target that makes sense for every organisation. Explain why a threshold is appropriate and what action follows if it is crossed.
Frameworks such as ISO 27001 and DORA can organise obligations differently. Map the obligations and controls relevant to your organisation before comparing results. Similar labels do not necessarily mean identical scope or evidence. A structured evidence-backed compliance measurement approach can help maintain traceability across mapped frameworks without treating one KPI set as automatically suitable for all.
Which compliance KPIs are most useful? Compare indicator types
The most useful measures depend on the decisions leaders need to make. A balanced set of key performance indicators for compliance management combines signals about future exposure with evidence of what has already happened. It also distinguishes activity, such as tests completed, from outcomes, such as weaknesses found and addressed.
Leading and lagging indicators in a compliance programme
Leading indicators can prompt preventive action. For example, the age of open remediation actions may signal that identified exposure is not being addressed. Define the scope clearly, including which actions count and how age is calculated. A lagging indicator, such as the number or type of control failures identified during a period, records an observed outcome and can help reveal recurring weaknesses.
Neither view is sufficient alone. Completed control tests show that testing activity took place, not that controls were effective. Pair forward-looking signals with observed outcomes, relevant test results and validated evidence. This helps prevent a favourable activity figure from disguising unresolved issues.
A comparison of common compliance KPI categories
Use the examples below as options to assess against your objectives and risk profile, not as universal targets or mandated KPIs.
Interpret measures together and investigate material changes. For example, more completed tests may increase the number of exceptions recorded. That could reflect stronger detection rather than deteriorating control. A balanced view makes the distinction visible and reduces the risk of one favourable KPI masking weak performance elsewhere.
How to put compliance KPIs into practice and report them
Start with a manageable set of key performance indicators for compliance management, selected around material risks, relevant obligations and the decisions leaders need to make. Too many measures can obscure priorities; too few may leave important exposure unexamined. For each KPI, assign responsibility for capturing the data, validating it, interpreting the result and escalating exceptions. Make these duties explicit, even where one person holds more than one role.
Report for different audiences without breaking the evidence trail. A board-level summary should surface material trends, exceptions, exposure and decisions required. Operational reporting can provide the underlying control detail, evidence gaps and remediation status. Both views should use consistent definitions and allow a reported result to be traced back to its source.
Build a repeatable KPI review cycle
Set the review frequency according to risk, the availability of reliable data and your organisation’s governance requirements. At each review, compare results with the agreed baseline and prior periods. Consider changes in scope, evidence quality and remediation context. A shift in the number might reflect a changed method or population, not improved performance.
Record exceptions, methodology changes, decisions and resulting actions. Assign each action an owner and follow-up point. Retire or redesign measures that no longer support decisions or cannot be evidenced reliably. Keeping a weak KPI can create false confidence rather than useful oversight.
Avoid misleading compliance dashboards
A green status is a prompt for interpretation, not proof. High completion rates can coexist with ineffective controls, while a small sample may not represent the full population. Display the scope measured, data freshness, evidence gaps and material limitations alongside the result. Without these details, readers may mistake an incomplete view for assurance.
Link each exception to the relevant evidence, accountable owner, decision and remediation path. Review trends alongside the underlying records, and escalate issues according to their significance and agreed governance process. This turns reporting into a control loop: measure, investigate, decide and track action.
Where evidence and reporting are spread across teams or frameworks, a structured compliance validation platform can help provide a consistent view of controls, supporting records and outcomes. The CWORT demonstration page explains how the platform can support evidence-backed compliance reporting.
How CWORT supports evidence-backed compliance KPI management
KPIs are only as reliable as the control definitions, evidence and assessment method behind them. CWORT is a compliance validation and operating-model platform that organises controls, binds evidence to control outcomes and presents an explainable view across mapped frameworks. It sits above existing security tools, helping teams bring compliance information into a structured view without replacing those tools.
This can help address a common reporting weakness: a result appears on a dashboard, but teams cannot readily trace it to the evidence and control it represents. CWORT supports evidence registers and delivery tracking, giving teams a basis for connecting assessment findings with accountable follow-through. Its deterministic scoring is reproducible: when the same evidence is assessed consistently, it produces the same result. This supports repeatable reporting, but does not prescribe which KPIs an organisation should use or guarantee compliance.
From fragmented tracking to traceable compliance measurement
Framework crosswalks can help organisations relate mapped controls to different frameworks and report from a shared assessment, while preserving the context of each framework. That matters because corresponding controls or requirements should not be assumed to have identical scope. Board-ready and audit-ready outputs can present a concise view of outcomes, with underlying evidence available to support review.
The June 2026 taxonomy snapshot records 1,355 controls across 217 domains and 42 frameworks or standards. Treat these as dated figures, not an assurance that every control applies to your programme. For a closer look at how CWORT structures controls and evidence, see the compliance validation platform.
Evaluate whether an orchestrated platform fits your programme
Before changing your workflow, check whether it can answer practical assurance questions:
- Can each reported KPI be traced to its scope, source evidence and relevant control?
- Can your team reproduce the result using the same evidence and assessment method?
- Are ownership and approval responsibilities clear, including separation of duties?
- Can you report across the frameworks relevant to your organisation without obscuring differences in scope?
If those answers are difficult to establish, review where evidence, ownership or reporting breaks down before selecting a platform. A programme-specific demonstration can help you assess whether CWORT’s control mapping, evidence registers and reporting outputs fit your requirements.
Make compliance reporting more defensible
Strong key performance indicators for compliance management connect defined objectives to control outcomes, traceable evidence and accountable action. Activity counts can show what teams have done, but they need to sit alongside measures of effectiveness, exposure and remediation to give leaders a balanced view.
Keep each KPI consistently defined, assign responsibility for its data and interpretation, and review changes in scope or evidence quality before drawing conclusions. Reporting is most useful when decision-makers can follow a result back to its source and understand what action it requires.
CWORT maps controls across frameworks and binds evidence to control outcomes. Its deterministic scoring is designed to produce reproducible results when identical evidence is assessed consistently. These capabilities can support a more traceable measurement process, while KPI selection remains grounded in your organisation’s objectives and risks.
Assess whether your current workflow can reproduce reported results and show the evidence behind them. Request a CWORT demonstration to explore how it may fit your programme. With clear measures and a reliable evidence trail, you can give leadership a stronger basis for oversight and prioritisation.
Frequently Asked Questions
Which KPIs should a compliance team track?
Choose KPIs that relate to your organisation’s material risks and the decisions leaders need to make, rather than adopting a generic list. Options include control-test coverage, evidence currency, overdue remediation and completion of required reviews. Select a small, balanced set that combines activity with outcome and effectiveness measures. Define each consistently, note its limitations and link it to supporting records. A high number of completed reviews, for instance, does not establish that the controls reviewed operated effectively.
How do you measure compliance programme effectiveness?
Define the intended outcome, assess relevant controls against clear criteria and examine the evidence supporting each assessment. Review results over time alongside exceptions, remediation progress and changes to the scope or method. A high completion rate alone is not proof of effectiveness: it shows activity, not necessarily whether a control worked. Document the measurement approach and its limitations so leaders and assurance teams can interpret what a result demonstrates and what it cannot establish.
Are compliance KPIs required by regulations such as DORA?
Do not assume that a particular KPI or target is universally required under DORA or another regulation. Whether a reporting obligation applies depends on the relevant requirements and the organisation’s circumstances. Treat KPIs as management measures unless an authoritative source specifies otherwise. Check current primary regulatory material and any applicable technical standards, then seek appropriate legal or compliance advice when interpreting duties. A useful internal KPI can support oversight without being a regulator-prescribed measure.
How often should compliance KPIs be reviewed?
Set review frequency according to the measure’s risk, purpose, data availability and governance cycle. Operational indicators may need more frequent attention than board-level summaries. Document the chosen cadence, and establish how material exceptions or changes will be escalated. Reassess the frequency when risks, obligations, control scope or data sources change. An arbitrary interval can make reporting either too slow to inform action or unnecessarily frequent for the decisions the KPI is meant to support.
Can compliance KPIs be automated without losing auditability?
Yes, automation can support consistent data collection, but auditability depends on preserving definitions, controlled data sources and a traceable record of changes. Retain the evidence and calculation context behind each result, including its scope and accountable owner. Validate automated outputs and investigate exceptions. Automation should make review more reliable, not turn an unexplained dashboard status into a compliance claim. Keep human oversight in the process so results are interpreted and acted on appropriately.
Disclaimer
The content on this site is provided for general information and educational purposes only. It does not constitute legal, regulatory, financial, or professional advice. CWORT provides AI-assisted insights and workflow automation, but all compliance decisions remain the responsibility of your organisation and its management. Always seek qualified legal or regulatory guidance for decisions relating to the UK NIS Regulations, CAF, DORA, NIS2, ISO 27001, or other obligations.
Related posts
Streamlining Regulatory Compliance Processes: From Manual Tracking to Orchestrated Validation
Stop wasting money on manual compliance. Learn about streamlining regulatory compliance processes to reduce personal liability under DORA & NIS2 and gain aud...
How to Demonstrate Control Effectiveness to Regulators: A Strategic Guide
Learn how to demonstrate control effectiveness to regulators with our guide. Shift from chaos to an evidence-based, audit-ready compliance programme today.
Real-Time Compliance Dashboards for Executive Decisions
See how real-time compliance dashboards for executives turn trusted data into clear risk signals, accountable actions and stronger regulatory oversight.
Article by
Michael Iyiola
Co-Founder, CWORT
Michael Iyiola is a co-founder of CWORT and a Cyber and AI Security Engineer with deep experience in vulnerability management, detection engineering and operational resilience across UK critical national infrastructure, including rail, energy and financial services. At CWORT, he designs scalable, evidence-driven workflows that help teams meet modern regulatory and security demands.
Build Your Foundation of Auditable Certainty
Take control of your regulatory obligations and secure your infrastructure with CWORT.